
Abstract
Organizations have never had more Application Security tools, frameworks, and technologies available than they do today. Yet many continue to struggle to demonstrate meaningful risk reduction and business value.
In a market flooded with AI-powered platforms, vendor promises, and ever-growing lists of “must-have” capabilities, it’s easy to mistake what looks impressive for what an organization actually needs. Over time, many organizations fall into the AppSec Decision Trap, equating a collection of security tools, or even a DevSecOps pipeline, with a mature Application Security program. The result is often increased complexity, higher costs, investments and AppSec initiatives that deliver far less value than expected.
The problem isn’t a lack of technology—it’s decision-making.
In this session, we’ll explore how OWASP SAMM can be leveraged not only to accelerate Application Security maturity, but also as a strategic compass for better decision-making. Through real-world stories and lessons learned from building AppSec programs across organizations of different sizes in financial industry, we’ll examine how SAMM helps distinguish between what an organization wants and what it truly needs—guiding smarter priorities, stronger investment decisions, and closer alignment with business objectives.
Because great AppSec programs are not built on better tools. They’re built on better decisions.
You’ll leave with a fresh perspective on Application Security strategy, a new way of thinking about OWASP SAMM, and practical insights to help you recognize—and avoid—the AppSec Decision Trap.
Speaker Bio
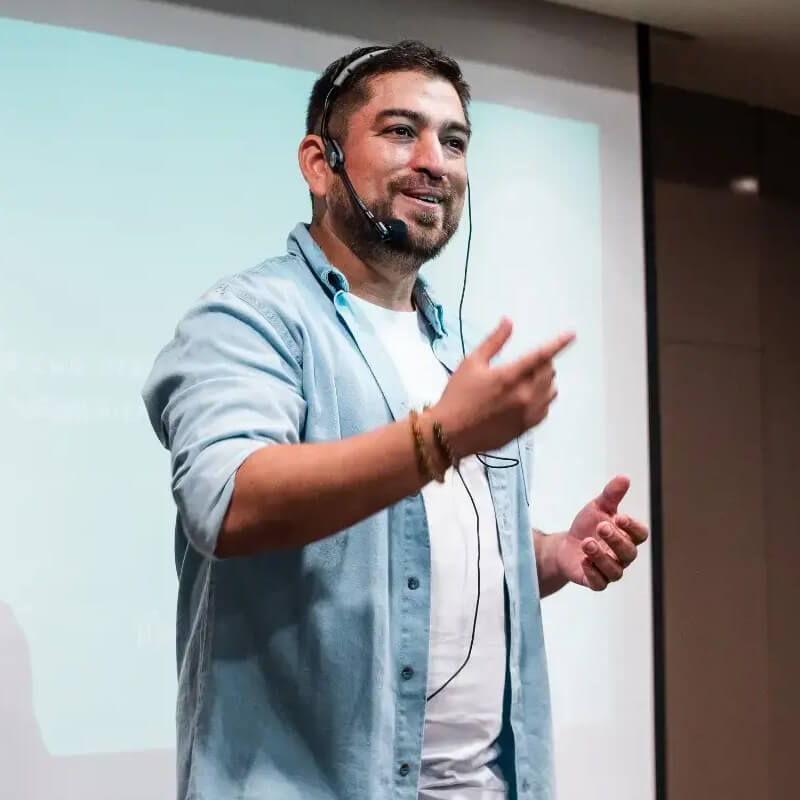
Max Alejandro Gómez-Sánchez Vergaray is an Application Security leader, consultant, and international speaker with nearly a decade of experience building and scaling AppSec programs in highly regulated environments. He designed and led the Application Security Program for one of Latin America’s largest financial institutions, embedding security into the software development lifecycle of more than 350 applications and enabling over 3,500 professionals through secure design, threat modeling, DevSecOps, and secure development practices.
Today, as the founder of LATAM AppSec, Max shares his experience helping organizations build sustainable AppSec capabilities aligned with business objectives. He is an active contributor to the OWASP community, collaborating on OWASP SAMM and OWASP Cornucopia, and led the official Spanish translation of OWASP Cornucopia. His talks focus on practical lessons learned from implementing AppSec at scale, covering AppSec strategy, Secure SDLC, Secure Design, Threat Modeling, Evil User Stories Modeling, and DevSecOps.